
121·
2 months agoYou review the open source code yourself.
You review the open source code yourself.
I wouldn’t consider them directly comparable since they are both trying to achieve different goals.
Linkwarden is a bookmark manager that allows for single html webpage backups.
Archivebox uses WARC - which produces an offline, fully navigable website
I see that as a generous interpretation. But to each their own.
I didn’t even mention the dude.
Right, which is why I said so I can block it. Not that it should be outright banned.
I’m just not interested in comics where the only ‘joke’ is slim thick mummy wants to fuck.
The comm needs to implement a gooner tag so I can block these.
Yeah, kinda. GamersNexus is popular for their no-bullshit PC benchmarking and their “indie” documentaries on anti-consumer behaviors tangentially related to gaming hardware.
The tldr is pretty much the title - the context is the video if you’re interested. The video may be long format but I don’t agree with what the other dude said about this being better served as an article. Steve (long hair dude) is pretty respectful of his consumer’s time. I think they post most of their videos as articles on their website too - ad free.

Mate you’re the only one whining. I got around the cookie banner just fine, and reposted here for others.
we share data with our 188 partners
That’s a no from me dawg
The updater integrated into Notepad++ has allowed itself to be infiltrated by malware, which has been installed on some PCs. The developer of the powerful open-source text editor is responding with an update to Notepad++ v8.8.9. Users currently have to perform the update manually.
In a news post on the Notepad++ website, developer Don Ho explains that “some security experts have reported incidents where internet traffic affecting Notepad++ was intercepted.” According to the post, investigations have revealed that traffic from the Notepad++ updater WinGUp “was occasionally redirected to malicious servers, leading to the download of compromised executable files.” IT security researcher Kevin Beaumont reports that at least three organizations “with interests in South Asia” have been targeted in this way.
As Beaumont explains, the updater uses a version check that queries the URL “https://notepad-plus-plus.org/update/getDownloadUrl.php” and evaluates an XML file delivered through it. The updater uses the download URL listed in the XML file, saves the file in the %TEMP% folder, and executes it. Anyone who can intercept and manipulate this traffic can therefore change the download URL. Until version 8.8.7 of Notepad++, the developer used a self-signed certificate, which is available in the Github source code. This made it possible to create manipulated updates and push them onto victims. Since v8.8.7, however, Notepad++ relies on a legitimate GlobalSign certificate, and installing its own Notepad++ root certificate is no longer necessary.
Remedy through updates
With Notepad++ v8.8.8, the WinGUp updater now forces github.com as the download source. Version 8.8.9, released overnight on Wednesday, further hardens Notepad++ and WinGUp so that they correctly check the signature and certificates of downloaded installers during the update process. If the check fails, the update process is aborted. Don Ho notes that investigations are ongoing to determine how the traffic hijacking occurred in the observed cases.
Kevin Beaumont also lists some indicators of compromise (IOCs). For example, connections from “gup.exe” to URLs other than “notepad-plus-plus.org”, “github.com”, and “release-assets.githubusercontent.com” are suspicious. Likewise, attention should be paid if “gup.exe” starts unusual processes – only “explorer.exe” and “npp*” related Notepad++ installers should run under it, which since versions 8.8.8 are also signed with a GlobalSign certificate. After the observed attacks, files named “update.exe” or “AutoUpdater.exe” (Notepad++ itself does not use these names at all) were apparently also found in the user’s TEMP directory, from which “gup.exe” downloaded and executed the updaters.
Notepad++ v8.8.8 currently does not find the update.
Beaumont recommends updating to at least Notepad++ v8.8.8. However, version 8.8.9 is even further hardened. The integrated updater from Notepad++ v8.8.8 does not yet find the update, and “winget” also does not currently find a newer software version. However, the latest version is available as a manual download on the Notepad++ website.
Notepad++ is frequently targeted by malicious actors because the software is popular and widely used. Last year, for example, Don Ho asked for help to get rid of a “parasitic website” that was creeping into the original Notepad++ site in Google search results. It had unscrupulous intentions. In general, fake sites often appear in search results offering virus-infected files.
(dmk)
This article was originally published inGerman. It was translated with technical assistance and editorially reviewed before publication.
Citation needed - but I suppose you could say the same about my claim.
I’d love to test this properly with an infrared thermometer but I don’t have one. All I have is an anecdote that I’ve been charging my OLED in it’s case since release and have never had an issue - not zipped up given the wire, just the lid flipped over on top.
I guess either way the BMS would prevent any real damage from occurring, which is why I say it’s a non-issue.
I can understand the concern. But a SD at full load would run significantly hotter, even with fan exhaust, than a powered-off SD charging in an enclosed case. It’s a non-issue.
Majority of the shirts in this community are just “shirts that may mildly amuse you”
I’ve been overseas a lot this year, and if anyone asks where I’m from my go-to response is “I’m American but I’m telling people Canadian.”
It’s a cheeky joke, without actually needing to lie about where I’m from, and is a clear indication that I don’t agree with the batshit crazy that’s going on in my country.
Yes. I’ve used this site before but I can’t guarantee how safe it is:
Poor guy asked for an .ipa file he can use with SideStore and still got linked to an .apk
Here, you’ll need to build it yourself or find an .ipa floating around: https://github.com/whoeevee/EeveeSpotifyReborn
If you trust me, a random stranger on the internet, I can send you the .ipa I have. But you’d be better off building it yourself.
Easy. D.
A. might have been a good answer but always remember to pay attention to the question’s phrasing.
Your childhood dog was the best boy. Current dog is the best boy.
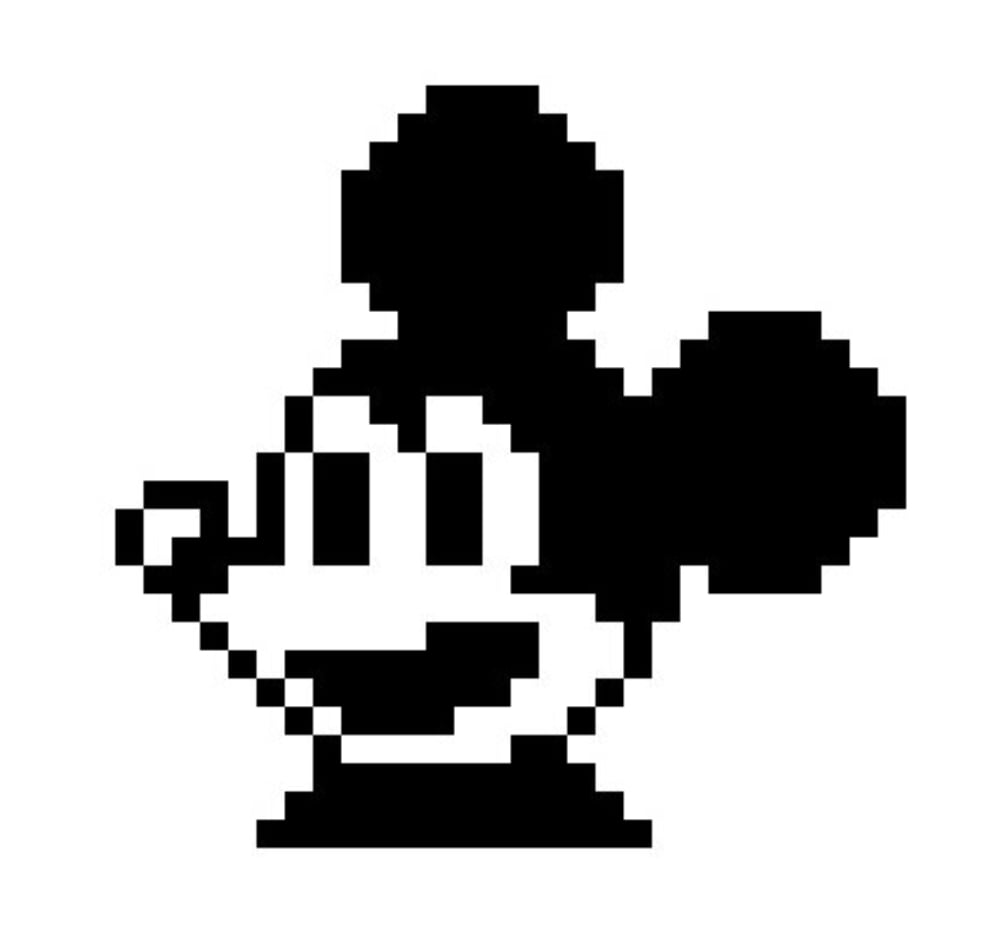
I feel this comic would land better if the conversation was happening between a different prey animal but not one that is preyed on by owls. A deer for example.
Eagles are also predators that would eat a mouse - so it doesn’t make a lot of sense in my mind, just my opinion though.
Brother, what? Their prophet Mohammed was a pedophile.
(No, this does not mean every Muslim is a pedo. But they’re certainly just as complicit with pedophilia as the Christians and Catholics.)

](safari-reader://www.heise.de/imgs/18/4/9/9/3/6/1/8/2025-12-10-Notepad__-8.8.8-Updater_findet_kein_Update-8f3a2396ab56758a.png)
I liked Sisu.
But that’s all that comes to mind.